智能体
x.com ·
@DeepLearningAI
DeepLearning.AI 介绍 Meta Muse agent 的 OS 层提示注入防御思路
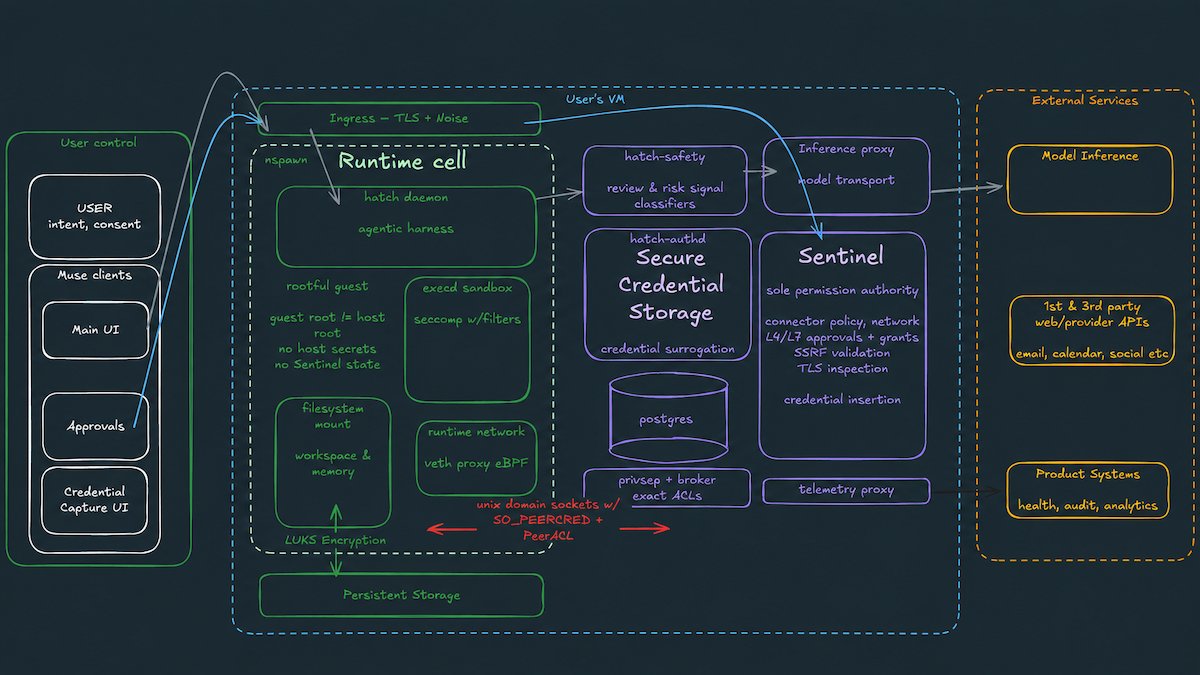
DeepLearning.AI 指出提示注入防御不应只依赖模型自身训练,并介绍 Meta 的 Muse agent 假设模型会被欺骗,转而在操作系统层构建安全机制:模型不接触真实凭证、工具在隔离的 Linux 容器中运行、由独立守门组件验证出站调用。
AI推荐理由 给出 Meta Muse agent 在 OS 层做提示注入防御的具体设计要点:模型不接触真实凭证、工具运行在隔离 Linux 容器、独立守门组件校验出站调用,属于可讨论的 Agent 安全架构信息;但来源为二手转述并附外链,未提供原始论文或实测数据,防御有效性未经证实。
74
浏览 2,522
点赞 48
评论 4
转发 5
正文
Prompt injection defenses shouldn't rely solely on a model’s own training.
Meta's Muse agent assumes the model will be tricked; instead, it builds security at the OS level.
🔑 Model never handles real credentials
🛡️ Tools run in isolated Linux containers
🛑 Independent gatekeeper verifies outbound calls
Read the full analysis[hubs.la/Q04xZx500](https://hubs.la/Q04xZx500)6V#DeepLearningAIg#AIAgentsn#AISecurityity